
Operating System
Cyber threats evolve daily, but internal safeguards remain your first line of defense. These 10 proven strategies empower cybersecurity leaders to fortify company data against breaches, leaks, and insider threats—without relying solely on external tools.
Role-Based Access Control Implementation
Tired of hearing about massive breaches caused by overprivileged accounts? Role-Based Access Control (RBAC) is the solution—it ensures employees only access what they need to do their jobs, no more, no less. This isn’t just theory: studies show 80% of breaches involve stolen or misused credentials, and RBAC cuts that risk dramatically.
Modern RBAC systems like Microsoft Azure AD or Okta let you define granular roles (e.g., "FinanceReadOnly" or "HRDataEntry") tied to job functions. Need to revoke access when someone leaves? Done in minutes. The real magic? Zero-trust principles baked in—no more "admin by default" culture. Tools like PingIdentity even integrate with SIEM platforms to flag unusual access patterns automatically.
This is a must for IT admins and compliance teams in regulated industries (think healthcare or finance). Start with a pilot in high-risk departments—like finance or legal—and watch your attack surface shrink. ✨
Automated Data Encryption for Sensitive Files
What if your most sensitive files—contracts, customer data, or proprietary research—were automatically locked down the moment they left your device? Automated data encryption does exactly that, turning your files into unreadable ciphertext without manual effort, whether they’re stored on a hard drive or transmitted across networks.
Modern solutions like BitLocker (Windows), FileVault (macOS), or VeraCrypt encrypt files using AES-256-bit or XTS-AES algorithms, ensuring even forensic experts can’t recover data without the decryption key. The best tools integrate seamlessly with cloud storage (e.g., Microsoft OneDrive, Google Drive) and enforce encryption policies company-wide, so lost laptops or intercepted emails remain secure. For added security, hardware-based encryption (like TPM chips) ties decryption to physical devices, preventing offline attacks.
This safeguard is non-negotiable for industries handling HIPAA-compliant health records or GDPR-regulated customer data, but it’s equally valuable for any business where data breaches could mean reputational damage or legal penalties. Implement it as your first line of defense against the #1 cause of data leaks: human error or device theft. ✨
Endpoint Detection and Response Deployment
Your devices are the frontline of cybersecurity—yet most antivirus tools only react after damage is done. Endpoint Detection and Response (EDR) flips the script by continuously monitoring every device for anomalies, stopping threats like ransomware before they even encrypt your files.
With real-time behavioral analysis, EDR solutions like CrowdStrike or SentinelOne detect suspicious processes, lateral movement, and data exfiltration attempts across endpoints. Features like automated containment isolate infected devices instantly, while forensic-ready logs provide clear evidence for investigations. Unlike traditional AV, EDR focuses on proactive hunting—not just signature matching.
This is non-negotiable for industries handling sensitive data, like healthcare or finance. Even small teams benefit from the peace of mind knowing their laptops, servers, and IoT devices are under 24/7 watch. ⚡
Regular Security Awareness Training Programs
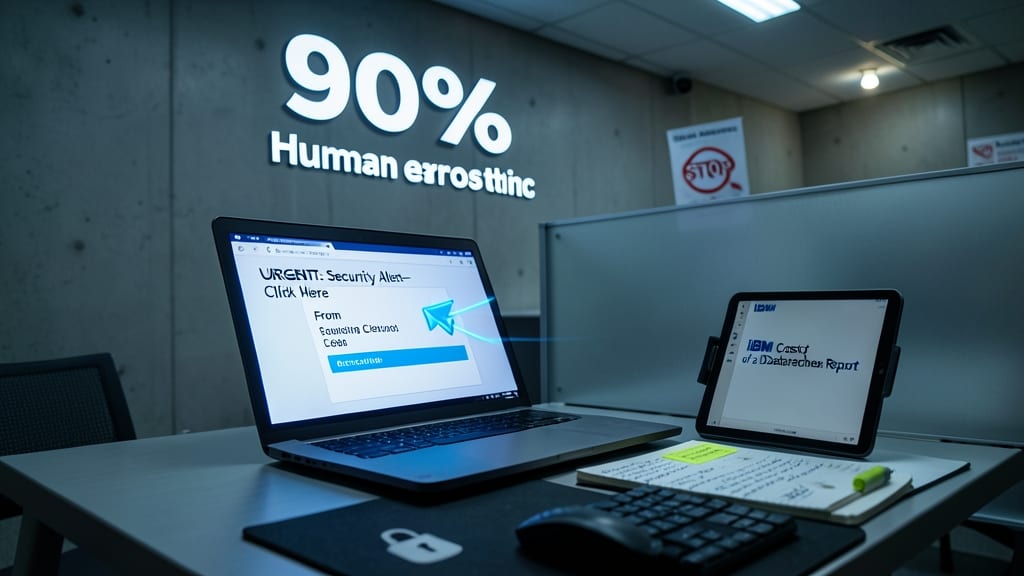
Most breaches start with a single click—yet 90% of cyber incidents involve human error, according to IBM’s Cost of a Data Breach Report. Security awareness training isn’t just another compliance checkbox; it’s the first line of defense against phishing, baiting, and pretexting attacks that bypass even the strongest technical controls.
Programs like KnowBe4’s Security Awareness Training or Proofpoint’s Simulated Phishing deliver quarterly simulations with real-world scenarios (e.g., fake invoice scams or CEO impersonations) to test and train employees. Interactive modules cover social engineering red flags, like urgent requests for sensitive data or mismatched email domains. Post-training assessments reveal vulnerabilities—like 30% of employees failing to spot a spear-phishing email in tests—highlighting where retraining is critical.
This isn’t just for IT teams—every employee benefits, from executives to interns. Industries handling PHI, PII, or trade secrets (healthcare, finance, legal) see the biggest ROI, but even small businesses reduce breach risks by 70% with consistent training. Start with monthly phishing tests and annual deep-dive workshops to keep defenses sharp. ✨
Multi-Factor Authentication for All Systems
Passwords alone are like leaving your front door unlocked—even if your key is secure, it’s still too easy for the wrong hands to get in. Multi-Factor Authentication (MFA) adds a second layer of defense, requiring a second verification step (like a fingerprint scan, hardware token, or one-time code) to access critical systems.
With 99.9% of successful breaches involving compromised credentials, MFA reduces unauthorized access risk by 96%—even if passwords are stolen. Modern solutions like Microsoft Authenticator or YubiKey integrate seamlessly with cloud platforms, VPNs, and internal apps, offering zero-trust compliance without disrupting workflows.
This safeguard is non-negotiable for industries handling PHI, PII, or financial data, but even small teams benefit from protecting remote access and admin panels. Start with high-risk accounts first—your IT team’s credentials should never be the weakest link. 💻
Insider Threat Monitoring with Behavioral Analytics
Not all threats come from outside your firewall—sometimes, the biggest risks sit right at your employees' keyboards. Insider threat monitoring uses behavioral analytics to spot subtle red flags, like a finance employee suddenly accessing HR payroll files or an IT admin downloading terabytes of data to a personal cloud account.
Modern solutions like Darktrace or Exabeam analyze patterns—such as unusual login times, rapid data transfers, or access to privileged systems—without relying on static rules. These tools learn your organization’s "normal" behavior, then flag deviations in real time, whether caused by malicious intent or careless mistakes. The key? Machine learning that adapts to evolving workplace dynamics, not just rigid policy checks.
Perfect for industries handling highly sensitive data (healthcare, finance, legal), this safeguard also helps companies comply with GDPR or HIPAA by proving due diligence against internal leaks. The best part? It catches threats before they escalate. 💡
Secure Document Management with Version Control
Imagine a scenario where a critical contract gets altered overnight by an insider—or a hacker—leaving your company exposed to legal or financial fallout. Version control for documents acts as an immutable audit trail, ensuring every change is tracked, timestamped, and recoverable in seconds.
Tools like GitLab’s document management or Microsoft OneDrive’s version history automatically save snapshots of files after edits, deletions, or even accidental overwrites. You can instantly revert to a previous version if tampered with, while change logs reveal who made edits and when—critical for compliance or investigations. For legal or financial teams, this means zero data loss during disputes or audits.
This safeguard is ideal for industries handling contracts, patents, or regulatory filings, where even a single unauthorized edit could have severe consequences. 💻
Network Segmentation to Isolate Critical Data
Imagine a breach happens—but instead of spreading like wildfire, it’s contained to a single segment of your network. That’s the power of network segmentation, a strategy that carves your infrastructure into isolated zones to limit damage and stop lateral movement.
By dividing networks into VLANs (Virtual LANs) or micro-segmentation zones, you create barriers that prevent attackers from jumping between systems. For example, your HR database might sit on a separate segment from guest Wi-Fi, ensuring even if one area is compromised, the other remains untouched. Tools like firewalls with stateful inspection and SDN (Software-Defined Networking) make this easier to manage than ever.
This approach is ideal for regulated industries (healthcare, finance) or any business handling sensitive data. It’s not just about stopping breaches—it’s about minimizing fallout when they happen. 💪
Automated Patch Management for Software Vulnerabilities
Outdated software is a hacker’s favorite entry point—yet many companies still rely on manual patching, leaving critical vulnerabilities exposed for days or weeks. Automated patch management flips the script by scanning systems for known flaws, downloading fixes, and deploying them before attackers can exploit them, often in under an hour.
Modern solutions like WSUS (Windows Server Update Services), Tanium, or SolarWinds Patch Manager integrate directly with your OS and third-party apps to prioritize patches based on risk. They handle zero-day updates, suppress unnecessary reboots during business hours, and even generate compliance reports for audits. The best tools also test patches in a sandbox first to avoid compatibility issues.
This is non-negotiable for IT teams managing hundreds of endpoints, but even small businesses benefit from reducing downtime caused by last-minute security updates. For companies handling sensitive data, automated patching is the quiet hero that closes gaps most attackers target first. ⚡
Incident Response Plan with Simulated Drills
When a breach happens, seconds matter—but most teams freeze. A pre-built incident response plan with quarterly simulated drills turns panic into precision, ensuring your team reacts like a well-oiled machine under pressure.
Start with a customized playbook outlining roles (e.g., containment, communication, forensics) and escalation paths. Then, run tabletop exercises—like a mock ransomware attack—where teams practice isolating systems, notifying stakeholders, and restoring backups. Tools like Splunk or IBM Resilient automate drill tracking, measuring response times and identifying gaps. The goal? Reduce mean time to detect (MTTD) and mean time to recover (MTTR) by 50% or more.
This isn’t just for Fortune 500s—even small teams benefit. Healthcare providers, fintech startups, or any business handling sensitive data should treat drills as mandatory as fire drills. 💪